
 Let's Talk
Security and Compliance, Built In
HIPAA, SOC 2 and PCI-DSS controls designed in from day one, with encryption, access control and audit trails your security team can verify.

Security & Compliance
Security is not an afterthought at Loku Digital—it’s built into everything we do. We adhere to HIPAA, SOC 2, and other U.S. compliance standards, ensuring your product is secure from day one. Our healthcare clients in Austin and Atlanta trust us to build platforms that handle sensitive patient data with the highest integrity. In fintech, we implement multi-layer security protocols, real-time monitoring, and role-based access control. We also assist with compliance documentation and audits as part of our full-service approach.
At Loku Digital, We Don’t Just Write Code — We Build Partnerships That Scale.
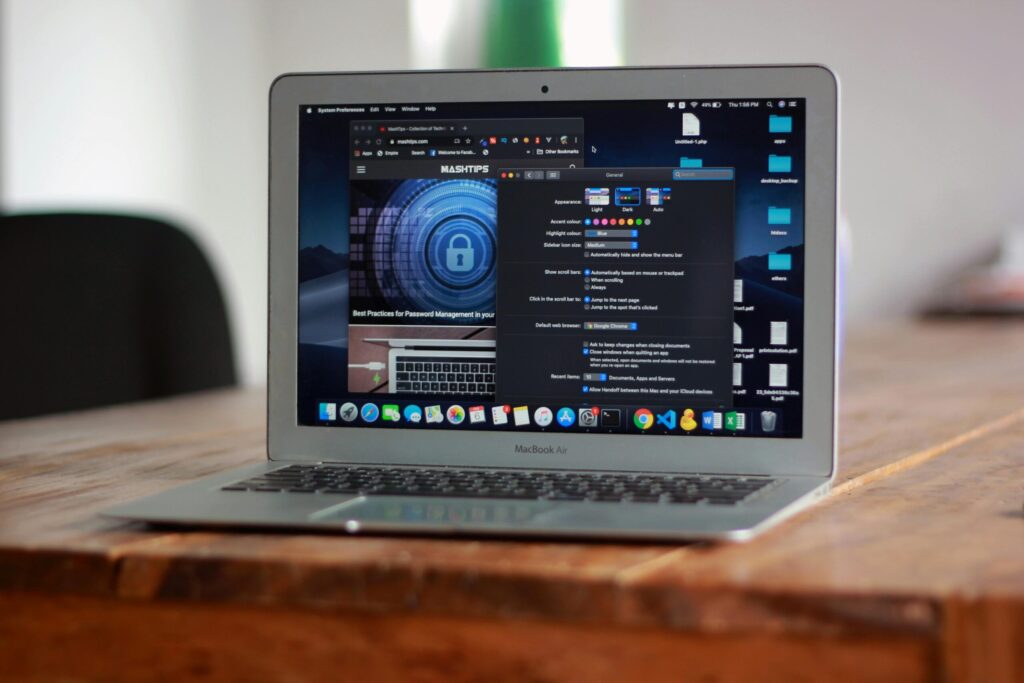
Built On Trust, Backed By Compliance
Our commitment to HIPAA, SOC 2, encryption, and secure access ensures that every solution we build is compliant, secure, and enterprise-ready—because our clients’ trust is everything.
HIPAA Compliance
We architect our systems with privacy in mind, safeguarding PHI across all endpoints, APIs, and user flows.
SOC 2 & Audit-Readiness
We help clients prepare for SOC 2 Type II audits by embedding logs, role tracking, and access control at every layer.
Data Encryption
From database to transport, all data is encrypted using AES-256 and HTTPS/TLS standards for enterprise-grade protection.
Access Management
Granular user permissions, multi-tenancy controls, and admin auditing ensure secure collaboration across teams.
Incident Response Planning
We implement breach response protocols, monitoring tools, and alert workflows tailored for HIPAA and fintech environments.
Vendor Security Assessments
Our partnerships are also vetted—we ensure our hosting, auth, and analytics providers meet U.S. compliance needs.
Compliance-First Development Offerings
Tailored software development services in Austin designed to meet the unique compliance needs of Fintech, Healthtech, and Enterprise SaaS.
HIPAA & SOC2 Alignment
API Gateways
Legacy Infrastructure Refactoring
Cryptographic Architecture
Smart Audit Logging
Why Strategic Partners Choose Our Security Framework
We combine the agility of an Austin based software company with the rigorous security protocols of a global enterprise. Our approach ensures that security is a business enabler, not a bottleneck.
Local Accountability
As a prominent software development company in Austin, we provide a level of transparency and face-to-face strategic consulting that offshore firms cannot match. We act as an extension of your team, providing local accountability for every security decision.
Full-Stack Sovereignty
Our software developers in Austin maintain complete control over the development lifecycle. We do not outsource your security; every line of code is written and peer-reviewed in-house to ensure no backdoors or unauthorized dependencies are introduced.
SecOps Automation
We don't just "check for bugs." Our austin tech consulting firm implements automated security-as-code. This proactive stance ensures that your platform automatically scales its defenses alongside its user base, maintaining peak performance under stress.
Risk-Mitigated ROI
We focus on the business impact of security. By identifying high-risk attack vectors early in the custom software development in Austin process, we prevent the catastrophic financial and reputational costs associated with post-launch data breaches.
Verified Compliance
We don’t just claim compliance; we prove it. Our software development services in Austin include the generation of real-time security telemetry and audit-ready documentation, making your next SOC2 or HIPAA certification a seamless formality.
Future-Proof Defense
The threat landscape changes daily. We utilize advanced heuristic monitoring and quantum-resistant encryption standards to ensure that the software we build today remains secure against the emerging threats of tomorrow.
Core Security Capabilities

System Hardening
Our austin software development company follows CIS Benchmarks to harden production environments. We minimize the attack surface by disabling unnecessary ports, enforcing “Least Privilege” access, and utilizing container scanning to find vulnerabilities in base images.

Zero-Trust Identity
We implement sophisticated Identity and Access Management (IAM) strategies. By leveraging OpenID Connect and hardware-backed MFA (WebAuthn), we ensure that user identity is verified through multi-layered cryptographic challenges at every entry point.

Traffic Encryption
We enforce TLS 1.3 for all data-in-transit and utilize Perfect Forward Secrecy (PFS). This ensures that even if a private key is compromised in the future, past communications remain encrypted and unreadable to attackers.

Heuristic Detection
We integrate AI-driven behavioral analysis that monitors your system for anomalous patterns. By establishing a “normal” baseline for API traffic and database queries, we can instantly trigger circuit breakers if suspicious bulk data-exfiltration is detected.
Have a prototype that needs to reach production?
Tell us where you are. A senior engineer will get back to you, with no sales pitch.
- Emailhello@lokudigital.com
- Phone+1 347-644-0405
- US headquarters12700 Ridgeline Blvd, Cedar Park
Austin, TX 78613 - Canada office15 Claridge Cres, Whitby
ON L1R 3E2 - HoursMon–Fri, 9am–8pm
Weekends, 10am–5pm